Compliance under control, end to end
Six complementary areas of expertise to secure your health data for the long term and turn compliance into an advantage.
GDPR compliance & data protection
Anticipate the risks, master the future.
From assessment to day-to-day operational follow-up, we cover every aspect of your GDPR compliance to secure your health data processing for the long term.
The 8 pillars of compliance
Outsourced DPO subscription
Confidence and peace of mind, day after day.
Outsource your DPO role for continuous, worry-free and simplified compliance management, with tailored support and effective tools.
The 7 keys to integrated compliance management
Advanced cybersecurity services
Protect, monitor, respond.
Strengthen the protection of your sensitive data: audits and technical measures delivered on a quoted basis by our cybersecurity partner, under our compliance co-supervision.
3 steps to strengthen your cybersecurity
Training & awareness
A culture of compliance, at every level.
Prepare your teams for compliance and security challenges with our advanced training courses, including ethical AI.
Artificial Intelligence (AI) support
Innovate with confidence.
Align your AI systems with the AI Act, the GDPR and the applicable frameworks — without slowing down innovation.
International & data transfers
Operate at global scale with complete security.
We help you navigate international regulations and secure your cross-border data transfers.
How does the engagement unfold?
Five steps, from the first conversation to the deliverables. At each step you know what you provide, what we examine and what you receive.
- 01Your organisation
You describe your situation
Your processing activities, tools, providers, projects — in plain facts, with no legal vocabulary. Your existing documents are reused, never re-entered.
- 02The DPO
Your DPO assesses
They complete the facts with you, clarify ambiguous cases, identify what is missing and what must be checked on the ground.
- 03NELSE
The technology qualifies
The legal regime of each processing activity is computed by sourced rules: DPIA required or not, derived obligations, points to assess — with the grounds displayed, replayable identically.
- 04The DPO and your management
Decisions are taken and traced
The DPO issues reasoned opinions and validates the records; your organisation keeps its management decisions. Each decision stays dated and reasoned, and whatever changes afterwards goes back to validation.
- 05Your organisation
You receive verifiable deliverables
An up-to-date register, a control file a third party can verify, a progress report readable by your board, an action plan — and the history of what was decided, by whom and when.
The outsourced DPO subscription includes your teams' access to the tool. For other offers, the precise terms — features used, exports delivered, possible access — are detailed in each proposal.
The technology our support relies on
Our support relies on the tools built by NELSE — a normative-engineering deeptech: law made executable through deterministic rules — proof, not probability. Where the market hands your register to a generative AI (while disclaiming any responsibility for the output), we do the opposite.
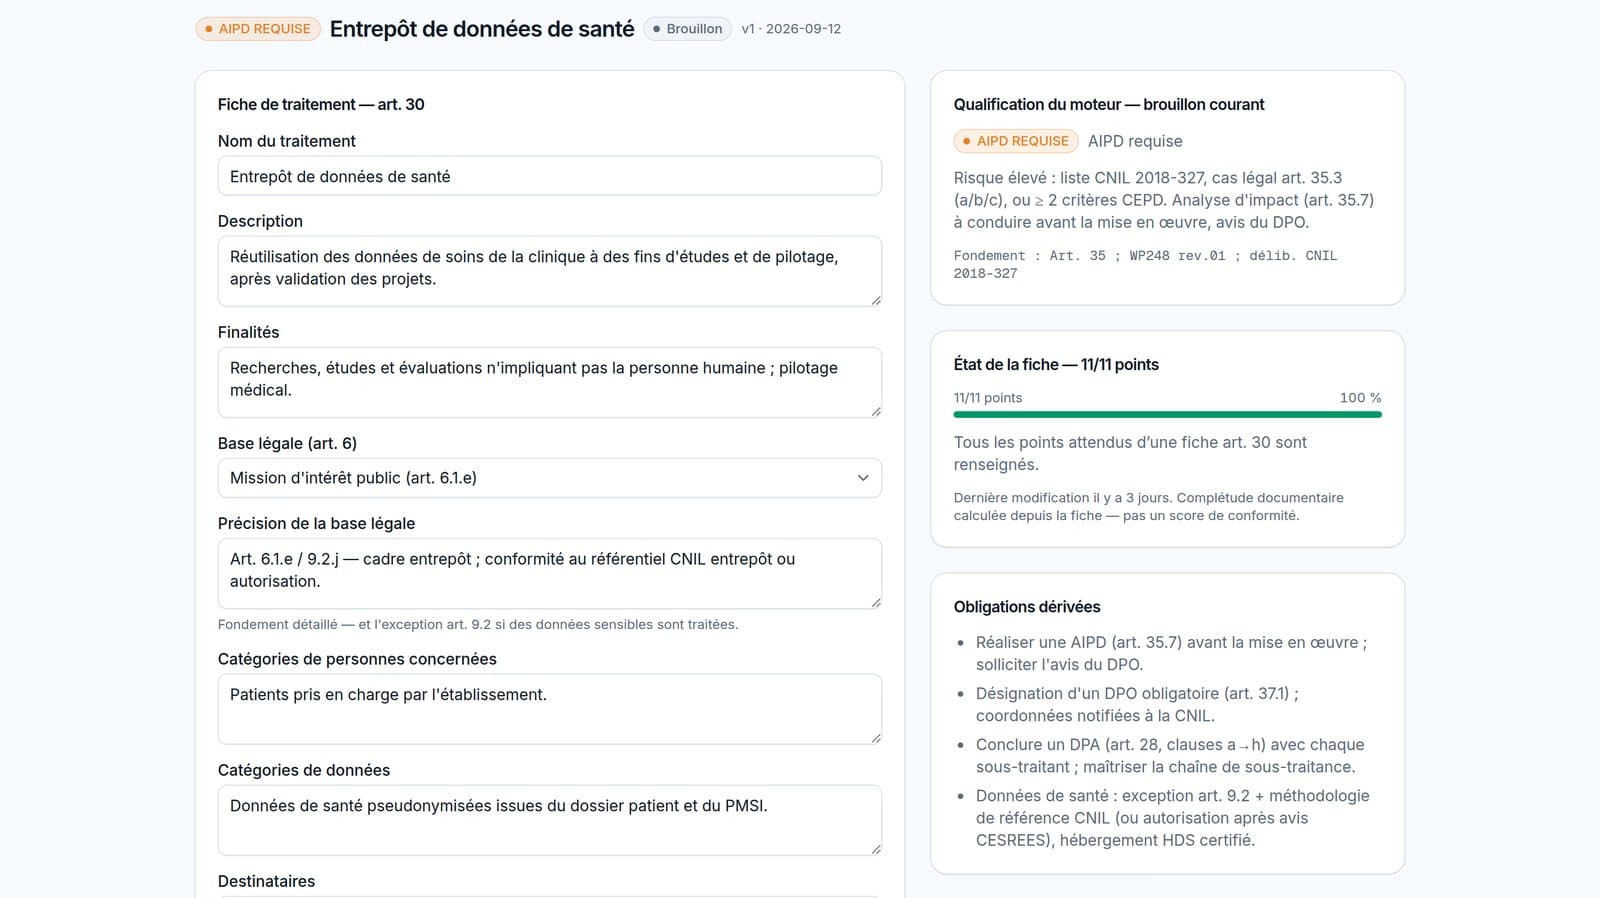
A register qualified by a rules engine
Every processing activity is analysed by written, sourced legal rules (GDPR, CNIL frameworks, HDS, AI Act): same facts, same result, rules displayed. Not a generative AI that “suggests” — a computation that can be replayed.
Files a third party can verify
The audit files we deliver are designed to be checked by a third party: your auditor, lawyer or supervisory body verifies their integrity without an account and without trusting us.
Reports generated from your data
Progress reports, transparency page, consolidated multi-site roll-up for groups: documents produced from your actual file and reviewed by your DPO — not templates filled in by hand.
Determinism guarantees the reproducibility of the computation, not legal infallibility: rules are sourced, opinions remain your DPO’s and decisions remain your organisation’s.
A specific need, a tailor-made response
Let’s talk about your context: together we identify the services suited to your situation and your priorities.
Response within one business day · No commitment